Software Engineer, Equity Strategist, Polymath.
Posts tagged modular blockchains
The Architecture of Modular Blockchains: Securing Data Availability in Distributed Systems
6 days
by Ray Tawil
in Blockchain
What happens when we split the monolithic blockchain stack?
Traditionally, blockchains operated on a monolithic architecture. A single network of nodes was responsible for handling all four core functions: Execution (running transactions and updating state), Settlement (resolving disputes and finalizing state), Consensus (ordering transactions), and Data Availability (ensuring all transaction data is published and accessible).
As decentralized networks scale, forcing every node to download, verify, and store every piece of data creates a severe throughput bottleneck. The industry’s answer has been to modularize. By decoupling the execution layer (through Layer-2 and Layer-3 rollups) from the underlying consensus and data layers, networks can process thousands of transactions per second off-chain. However, this decoupling introduces a critical vulnerability: how do we prove that the off-chain data actually exists and remains accessible to everyone?
The Data Availability (DA) Problem: Why consensus is not enough
The “Data Availability Problem” is a security challenge unique to modular architectures. When a rollup (execution layer) processes a batch of transactions, it state-transitions off-chain and posts a summary (or “state root”) to the base settlement layer.
But what if the rollup sequencer—the party responsible for bundling and submitting those transactions—posts the new state root but refuses to publish the transaction data used to calculate it? This is known as a data withholding attack.
Without the transaction data, users and external validators cannot recalculate the state to verify that the transactions are valid, nor can they reconstruct their account balances. In a fraud-proof (Optimistic) system, they cannot challenge fraudulent transactions because they lack the evidence. In a validity-proof (ZK) system, they cannot withdraw their funds if the sequencer goes rogue.
Simply having consensus that a block is “valid” does not guarantee that the transaction details are available. In modular design, data availability is the foundation of security.
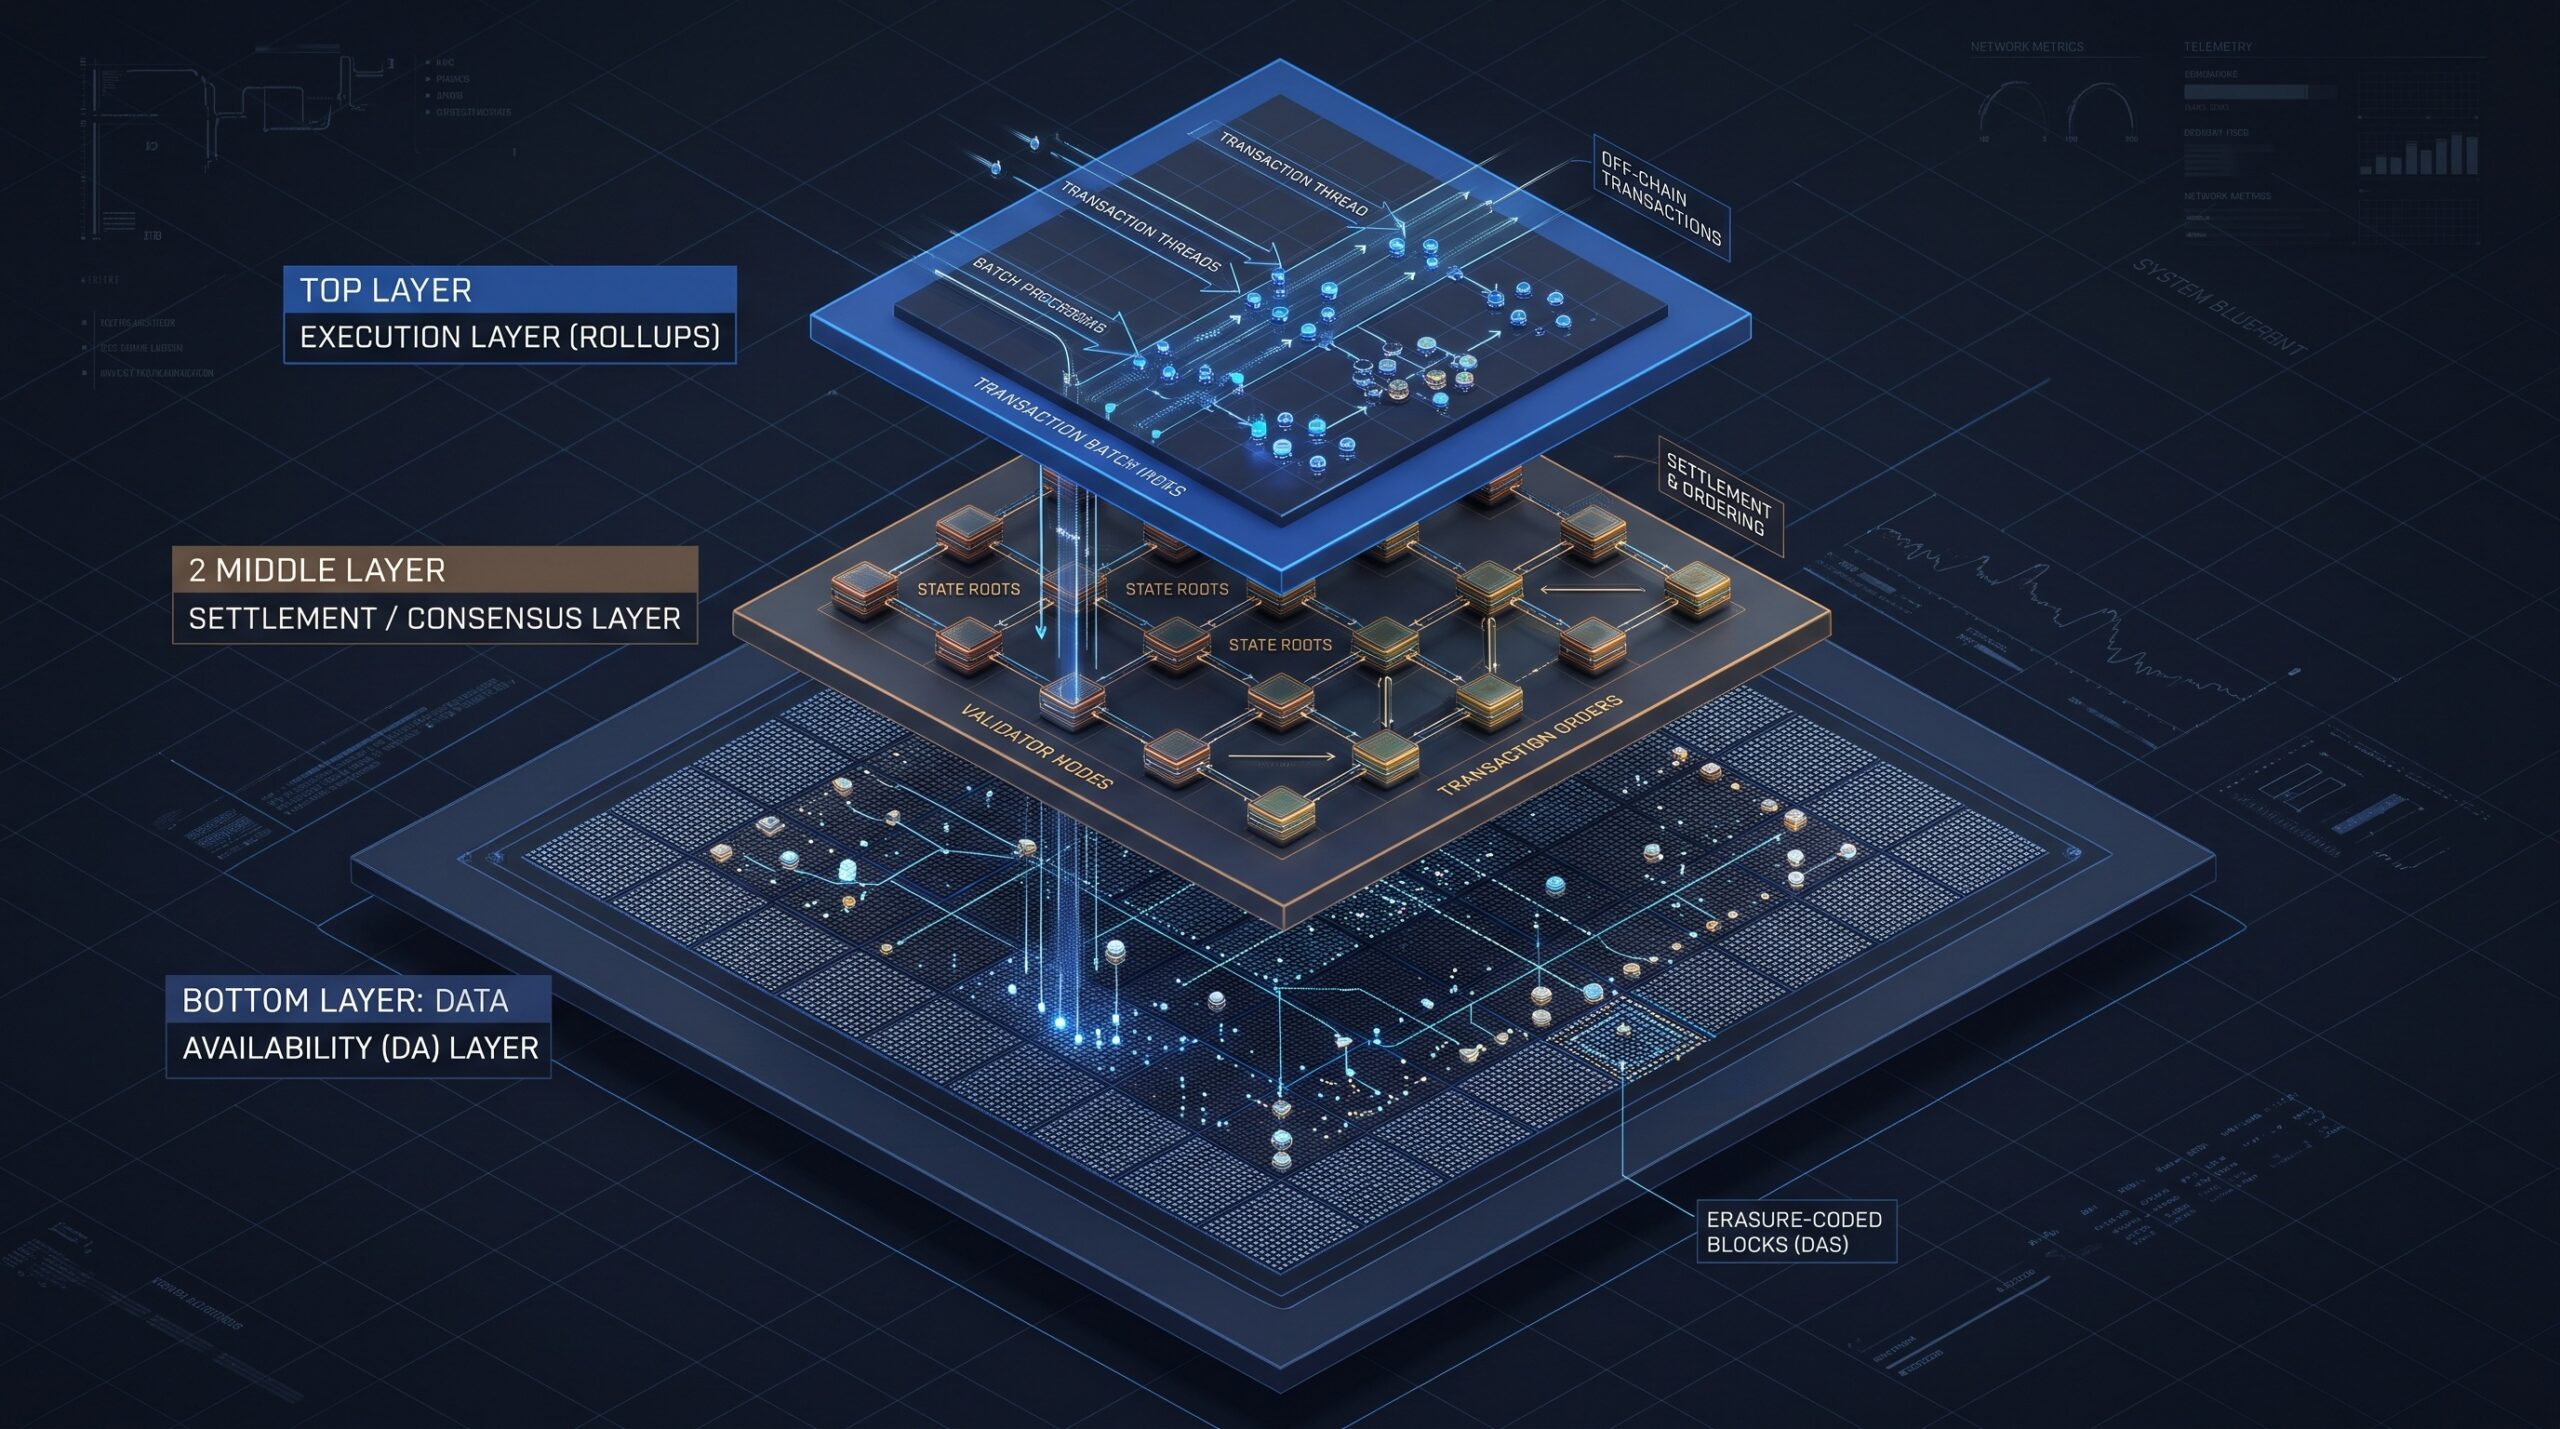
How Modular Networks Secure Data Availability: Erasure Coding and Sampling
Rather than forcing every validator to download entire transaction datasets, modern modular networks (like Celestia, EigenDA, and Ethereum’s blob space) rely on advanced cryptography to verify that data is publicly available without requiring exhaustive downloads:
- 2D Reed-Solomon Erasure Coding: Before data is published, it is split into pieces and “erasure-coded” into a larger mathematical matrix. This is the same math used in DVDs and spacecraft communications to recover lost signals. By expanding the data, it ensures that even if a malicious actor tries to hide up to 50% of the data, the entire original dataset can be reconstructed using the remaining 50%.
- Data Availability Sampling (DAS): Light clients (ordinary users or lightweight nodes) can perform DAS by randomly requesting tiny, randomized chunks of the expanded matrix. If a light client requests a handful of random samples and they are successfully provided, the probability that the data is complete approaches 99.99% within just a few rounds. This allows hundreds of decentralized, low-resource nodes to collectively verify data availability in seconds, without downloading massive blocks.
By transforming a “data downloading” problem into a “probabilistic sampling” solution, modular systems can securely expand transaction capacity while ensuring the underlying state remains verify-able and censorship-resistant.